TLDR:
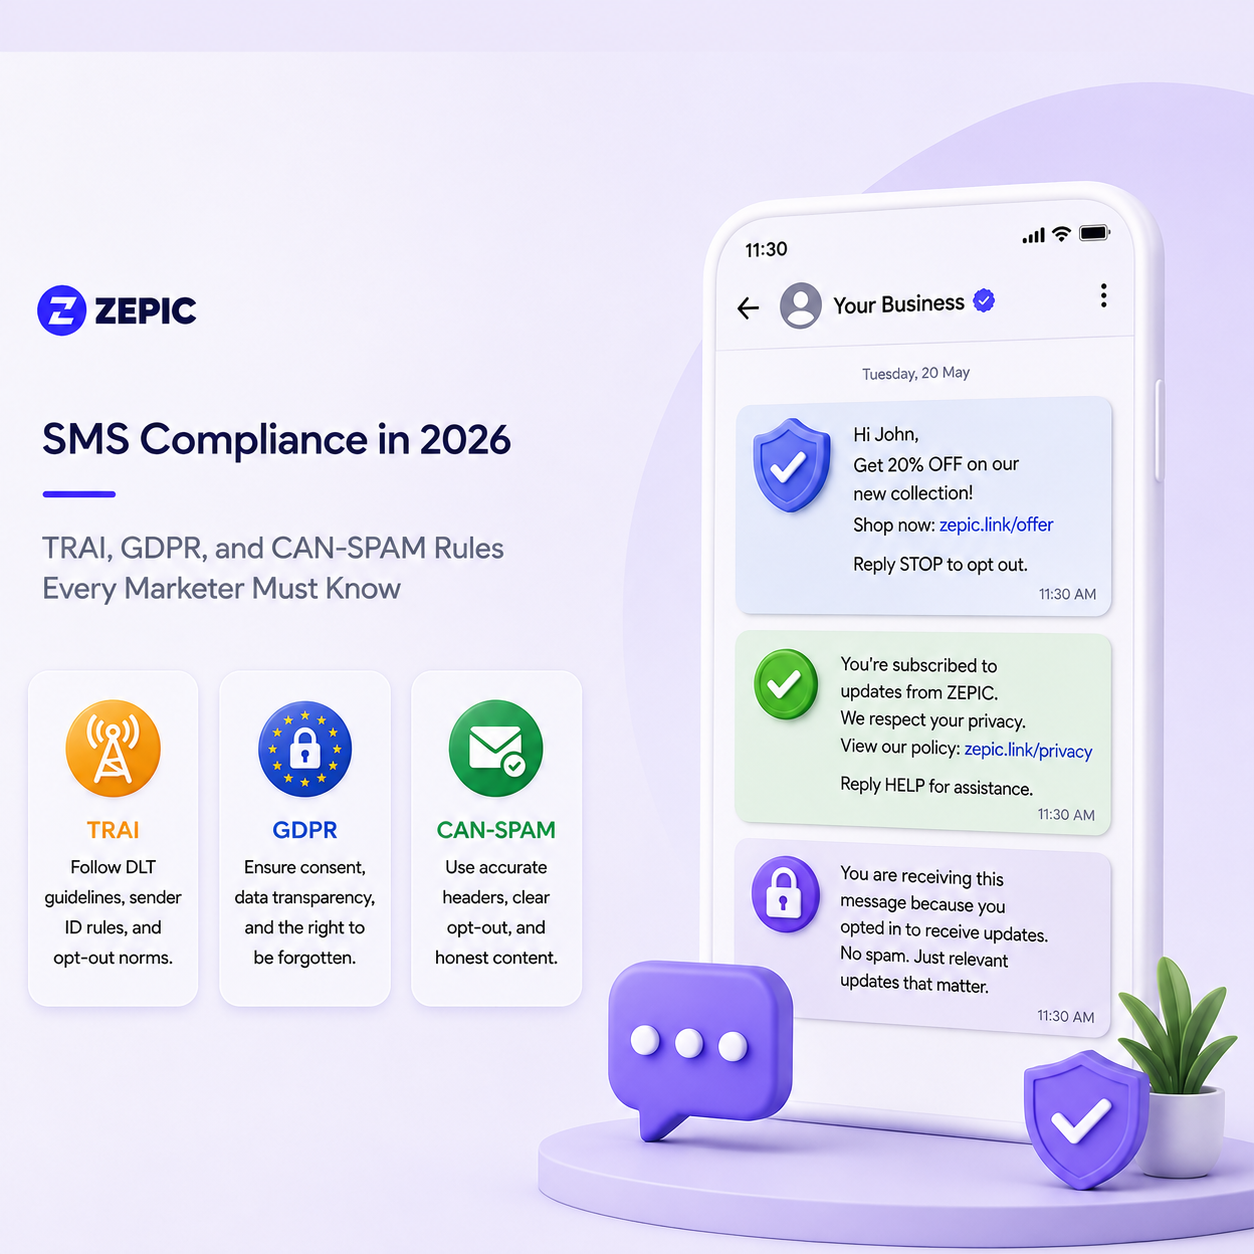
- India (TRAI): Runs on Distributed Ledger Technology (DLT). Requires Principal Entity + Header registration, pre-approved message templates, pre-tagged variable fields, and mandatory category suffixes.
- India timing/DND: Promotional SMS only 10 AM–9 PM; must scrub against the national DND registry before sending; transactional messages (OTPs) are exempt from time limits.
- EU (GDPR): Requires explicit, unbundled, unchecked-by-default opt-in — no implied consent, and SMS consent can't be bundled with email or T&Cs.
- EU opt-out & records: Withdrawal must be as easy as opt-in (e.g., "Reply STOP"), processed immediately, with full audit trails (timestamp, source, disclosure text, message history).
- US (TCPA/CAN-SPAM): Requires prior express written consent, plus the new one-to-one consent rule — no more shared/co-registration lists.
- US message requirements: Accurate sender ID, clear ad disclosure, physical postal address, and fast opt-out processing (carriers enforce instant STOP; CAN-SPAM allows up to 10 days).
- US carrier filtering (SHAFT): Content on Sex, Hate, Alcohol, Firearms, Tobacco/cannabis gets blocked at the network level regardless of consent — risking 10DLC/short code termination.
- Penalties are steep: $500–$1,500 per text (TCPA), up to 4% global turnover or €20M (GDPR), and DLT/PE deactivation with fines (India).
SMS marketing continues to maintain an exceptionally high engagement rate, with global industry metrics demonstrating open rates as high as 98%. Because consumers read text messages almost immediately, international regulatory bodies enforce rigorous frameworks to eliminate mobile spam and secure user privacy.
Navigating the regulatory landscape requires a clear understanding of the specific requirements enforced by the Telecom Regulatory Authority of India (TRAI), the European Union General Data Protection Regulation (GDPR), and the United States CAN-SPAM Act, along with the Telephone Consumer Protection Act (TCPA).
So let’s look at all these regulations and what you need to do.
TRAI SMS Compliance Rules in India: The DLT Ecosystem
The Telecom Regulatory Authority of India (TRAI) enforces one of the most technologically advanced messaging validation frameworks in the world. This system relies on Distributed Ledger Technology (DLT), which is a blockchain-backed infrastructure designed to track every commercial message from origin to delivery. In 2026, TRAI continues to refine these guidelines to close loopholes previously exploited by unverified senders.
Mandatory Principal Entity and Header Registration
Every enterprise planning to communicate via SMS in India must complete clear registration milestones on an approved DLT portal:
- Principal Entity (PE) Registration: Companies must submit verified corporate documents, corporate identification numbers, and tax registration details to establish a legal identity on the network.
- Header and Sender ID Approval: Brands must register unique alpha-numeric sender IDs. These headers are restricted to a maximum of six characters for promotional messages, allowing consumers to identify the source instantly.
- Template Matching Architecture: Every message broadcast must match a pre-registered template. The DLT system validates both the fixed text and the specific variable parameters before letting the message pass to telecom operators.
Pre-Tagging and Mandatory Category Suffixes
A significant regulatory update targets template manipulation. Scammers previously exploited the blank variable spaces inside approved templates to insert malicious links or fraudulent text. To counter this vulnerability, TRAI mandates explicit pre-tagging of all dynamic fields.
Furthermore, all commercial messages must feature a mandatory suffix indicating the exact category of the text. Consumers can identify whether an incoming message is a promotional advertisement, a critical banking alert, or an official service update based on this clear tag. If a brand attempts to send an SMS without the appropriate category suffix, carrier filters reject the transmission automatically.
Promotional Timing and DND Boundaries
TRAI maintains clear boundaries regarding when and how brands can deliver marketing content to consumers:
- Time Windows: Promotional text messages are restricted to a specific daytime window between 10:00 AM and 9:00 PM local time. Transactional messages, including one-time passwords (OTPs) and shipping updates, are permitted at any hour.
- National Do Not Disturb (DND) Registry: Before dispatching any promotional campaign, automated systems must scrub the target phone numbers against the national preference registry. Sending marketing material to a user who has registered for DND access results in heavy financial penalties and eventual blacklisting of the brand's Principal Entity status.
GDPR SMS Compliance: European Standards for Personal Data
The European Union's General Data Protection Regulation (GDPR) treats mobile phone numbers as highly sensitive personal data. If your organization communicates with subscribers residing in the European Economic Area (EEA), your mobile marketing strategies must conform to strict privacy principles. Under GDPR, processing personal data for direct marketing requires a clear, verifiable lawful basis.
The Standard of Explicit Opt-In Consent
GDPR completely eliminates passive or implied consent mechanisms. Marketing teams must secure clear consent before adding a person to an SMS marketing database:
- No Pre-Ticked Boxes: Checkboxes on landing pages must remain unchecked by default. The consumer must take a deliberate physical action to opt into the program.
- Unbundled Agreements: Consent for receiving text advertisements cannot be bundled into general terms of service or privacy policies. It must stand completely separate from account creation or purchasing agreements.
- Channel-Specific Permissions: Agreeing to receive email newsletters does not grant permission to send text messages. Senders must display distinct consent mechanisms for each communication medium.
Seamless and Instant Consent Withdrawal
A fundamental rule of European data law states that withdrawing consent must be as simple as granting it. If a user joins a list via a web form, they must have a straightforward path to remove themselves. For mobile communication, this is managed through clear text commands.
Brands must include explicit opt-out instructions within their message copies. Common implementations include adding phrases such as "Reply STOP to opt out" to the end of marketing broadcasts. G
DPR mandates that when a consumer initiates an opt-out request, the marketing platform must process the suppression immediately. Keeping a consumer on an active broadcast list after they request removal violates core compliance statutes.
Verifiable Audit Trails and Documentation
Data protection authorities require enterprises to maintain rigorous recordkeeping systems. If a compliance audit occurs, your organization must show clear proof of consent for every mobile number in the system. Essential data points for your compliance logs include:
- The exact timestamp showing the date, time, and timezone of the opt-in action.
- The specific digital channel or web form URL where the user submitted their number.
- The precise disclosure text the subscriber viewed before providing consent.
- The historical record of all outbound messages sent to that specific subscriber.
The United States Framework: Navigating TCPA and CAN-SPAM Rules
In the United States, SMS compliance is governed by a combination of federal statutes, Federal Communications Commission (FCC) orders, and strict carrier network rules.
While the CAN-SPAM Act primarily regulates commercial email, its specific wireless rules apply directly to text messages transmitted via internet-to-phone mechanisms, such as email-to-SMS gateways.
The Telephone Consumer Protection Act (TCPA) dictates the legal framework for standard phone-to-phone SMS communications.
Prior Express Written Consent and the One-to-One Rule
The cornerstone of US text messaging compliance is prior express written consent. Marketers cannot send automated commercial text messages without obtaining clear authorization that states the recipient agrees to receive marketing texts from a specific brand.
A critical regulatory update from the FCC enforces the strict one-to-one consent standard. This rule effectively dismantles the legacy practice of using co-registration or shared lead-generation lists.
In the past, a consumer checking a single box might accidentally consent to receive text messages from dozens of affiliated marketing partners. Under current rules, consent must be gathered individually for each distinct brand. Shared or bundled consent across multiple advertisers is illegal, meaning organizations must rely entirely on first-party opt-in methodologies.
CAN-SPAM Rules for Mobile Service Commercial Messages
When commercial text messages fall under the scope of CAN-SPAM's wireless rules, several explicit design requirements become mandatory:
- Accurate Header Information: Senders must use accurate sender details that clearly identify the business sending the campaign. Fake or hidden sender identities are not allowed.
- Clear Advertisement Disclosure: The message content must explicitly indicate that the communication is a promotional advertisement or a commercial offer.
- Physical Postal Address: Every commercial message must include a valid physical postal address of the business. This can be a physical street address or a properly registered Post Office Box.
- Prompt Opt-Out Processing: CAN-SPAM establishes a maximum threshold of 10 business days to honor unsubscription requests. However, mobile network infrastructure operates under much faster expectations. Mobile carriers enforce instant processing for standard opt-out keywords like STOP, QUIT, or UNSUBSCRIBE.
Carrier Controls and Prohibited Content (SHAFT)
Beyond federal legislation, the Cellular Telecommunications and Internet Association (CTIA) sets operational guidelines that US telecom carriers enforce through aggressive automated filtering. Even if a business possesses explicit written consent, certain content categories are strictly blocked at the network level.
Marketers must avoid what the industry defines as SHAFT content:
- Sex or adult-oriented material.
- Hate speech or discriminatory messaging.
- Alcohol promotions that lack age-gating mechanisms.
- Firearms or weapons advertisements.
- Tobacco, vaping, and cannabis products.
Because cannabis and CBD remain regulated under federal frameworks, carriers block text campaigns promoting these products regardless of local state legalities. Violating SHAFT restrictions can trigger immediate termination of a brand's 10-Digit Long Code (10DLC) or dedicated short code registration.
Global Compliance Matrix: TRAI vs. GDPR vs. US Framework
| Regulatory Element |
India (TRAI) |
European Union (GDPR) |
United States (TCPA & CAN-SPAM) |
| Primary Framework |
Distributed Ledger Technology (DLT) |
Article 6 Lawful Basis & Privacy Rules |
Federal Statutes & FCC One-to-One Consent |
| Consent Requirement |
Explicit registration via DLT consent templates |
Explicit, unbundled, affirmative opt-in |
Prior express written consent |
| Permitted Sending Hours |
10:00 AM to 9:00 PM for promotional texts |
Not federally restricted, but local quiet hours apply |
8:00 AM to 9:00 PM recipient local time |
| Opt-Out Processing Window |
Immediate system suppression |
Immediate processing |
Real-time for carrier keywords; up to 10 days under CAN-SPAM |
| Mandatory Identifiers |
Registered Header ID and category suffix |
Clear brand identity disclosure |
Accurate sender data and physical postal address |
| Financial Risk Profile |
Telecom service disconnection and structured fines |
Up to 4% of global annual turnover or €20 million |
Statutory damages from $500 to $1,500 per individual text message |
The Importance of Choosing the Right Marketing Platform for SMS
Regulatory knowledge only protects a brand if the underlying technology can actually enforce it. Given how differently TRAI, GDPR, and the US framework each define consent, timing, and recordkeeping, the platform sending your messages needs to do far more than deliver text at scale. It needs to act as a compliance layer in its own right.
Built-in consent management: A capable platform should track consent at the individual, channel, and brand level automatically, separating email opt-ins from SMS opt-ins. Retrofitting this after a campaign has already gone out is far riskier than choosing a platform that enforces it from day one.
DLT and template governance for India-bound campaigns: For brands messaging Indian numbers, the platform should support Principal Entity and header registration workflows, enforce pre-tagged dynamic fields, and prevent a campaign from launching without an approved template and category suffix. Without this, a single unregistered header can get an entire sender ID blacklisted.
List hygiene and deliverability tools: Platforms that support routine scrubbing for disconnected or reassigned numbers reduce both wasted spend and TCPA litigation risk, since messaging a reassigned number without renewed consent is a common source of legal exposure.
Unified, omnichannel consent records: Because SMS rarely operates in isolation from email and other channels, a platform that centralizes consent across channels in one system of record makes it far easier to prove compliance and avoid contradictory opt-in states between channels.
In short, the right platform doesn't just send messages; it enforces the guardrails these regulations require, so compliance becomes a byproduct of normal operations rather than a separate, error-prone process layered on top.
Actionable Checklist for Global SMS Compliance
Maintaining perfect compliance across multiple international borders requires an intentional, systems-driven approach. Marketing organizations can protect their deliverability rates and brand reputation by adopting these foundational operational strategies:
- Implement Robust Double Opt-In Flows: When a user enters their mobile number on a web form, trigger an automated confirmation text requesting an affirmative reply, such as texting back the keyword YES. This verifies that the mobile number belongs to the individual completing the form and confirms their explicit intent.
- Enforce Clean 10DLC Registration: For campaigns targeting United States consumers, ensure all business identities, sending numbers, and specific message use cases are registered through The Campaign Registry. Unregistered long codes face aggressive carrier filtering, often dropping message delivery rates down to 60%.
- Establish Regular List Hygiene Routines: Systematically scrub your subscriber databases to identify and remove inactive or disconnected phone numbers. This practice prevents your campaigns from accidentally messaging reassigned numbers, which is a frequent source of TCPA litigation.
- Centralize Omnichannel Consent Logs: Avoid siloed data management systems. Maintain a unified data repository that updates opt-in and opt-out preferences in real-time across text, email, and voice channels to ensure compliance across all active platforms.
By prioritizing structured consent, maintaining clear sender data, and respecting regional time boundaries, modern marketing teams can leverage the undeniable power of SMS communication safely and effectively.
Wrapping Up
SMS remains one of the most direct and effective channels a brand can use, but only when it's built on a foundation of genuine consent, regional compliance, and disciplined recordkeeping. TRAI's DLT infrastructure, GDPR's explicit opt-in standards, and the US framework's one-to-one consent rule all point to the same underlying principle: compliance is an ongoing operational discipline. The brands that treat it that way are the ones that protect both their deliverability and their customers' trust.
That discipline starts with the platform behind your campaigns. If your current stack can't enforce consent, timing, and suppression automatically, compliance will always be a manual afterthought, and manual processes are where violations happen.
SMS is coming soon to ZEPIC. If you're already using ZEPIC to orchestrate email, Instagram, and WhatsApp, native SMS will let you bring that same unified, consent-aware approach to text, all from one platform.
Stay tuned, or reach out to the ZEPIC team to get early access when SMS launches.
Frequently Asked Questions
Does CAN-SPAM apply to text messages sent from mobile phones?
The CAN-SPAM Act applies to commercial electronic messages, including certain text messages transmitted using internet-to-phone technology, such as messages sent from a computer or email address through wireless carrier gateways. Traditional phone-to-phone SMS messages sent over cellular networks are primarily regulated by the Telephone Consumer Protection Act (TCPA). Regardless of the applicable regulation, businesses must clearly identify themselves and provide recipients with a simple way to opt out of future messages.
What are the penalties for non-compliant SMS marketing in 2026?
Penalties for SMS marketing violations can be substantial and are often assessed on a per-message basis. Under the TCPA in the United States, businesses may face statutory damages ranging from $500 to $1,500 for each non-compliant text message. GDPR violations in the European Union can result in fines of up to €20 million or 4% of an organization's annual global turnover, whichever is greater. In India, TRAI regulations may lead to financial penalties as well as suspension of DLT headers and Principal Entity registrations.
Can a business buy a phone number list for SMS marketing campaigns?
Purchasing phone number lists for SMS marketing presents significant legal and compliance risks. Regulations such as the TCPA and GDPR require businesses to obtain explicit consent directly from each individual before sending promotional text messages. Since purchased lists do not provide brand-specific consent, using them can result in carrier filtering, legal enforcement actions, financial penalties, and reputational damage.
How long must an organization retain SMS consent records?
The required retention period depends on applicable regulations. In the United States, businesses commonly retain SMS consent records for at least five years to support potential TCPA claims. Under GDPR, organizations should maintain consent records for as long as personal data is processed and for any additional period required to satisfy legal or regulatory obligations. Maintaining detailed records—including timestamps, IP addresses, and the original consent source—helps demonstrate compliance during audits or legal disputes.